(NAIROBI, KENYA) – Kenya has proposed new rules requiring mobile money providers to report cyber theft immediately, as official data shows half of the KES 1.59 billion ($12.3 million / £9.3 million) stolen from banks by hackers in 2024 occurred through mobile banking.
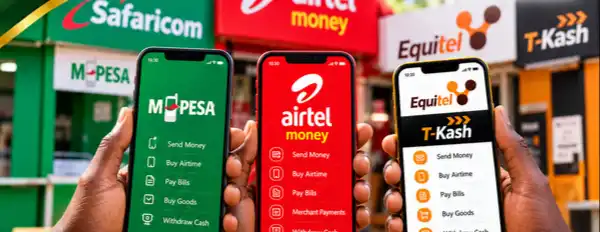
Under proposals from the Treasury and Central Bank of Kenya, payment service providers and payment system operators must notify the regulator of any cyber breach affecting their operations. This covers consumer-facing platforms such as M-Pesa and Airtel Money.
Providers that fail to report material incidents could face fines of up to KES 1 million ($7,750 / £5,860) or risk having their permits revoked.
“A payment service provider or a payment system operator that fails or refuses to comply, or gives false information relating to the material event, shall be liable to administrative enforcement action by the Central Bank,” the proposals state.
A material event is defined to include a significant data breach or cybersecurity incident, a prolonged or systemic service outage affecting payment processing or settlement, and the loss, unauthorised access to or misappropriation of customer funds. The framework aims to give authorities early warning of attacks that could disrupt financial services.
The push follows a sharp rise in cyber threats. Interpol data shows Kenya lost $3.8 million (KES 492.3 million) in cash and cryptocurrency to SIM swap fraud in 2025, with incidents rising 327%. More than 123,000 fraudulent SIM cards were issued, enabling criminals to hijack victims’ phone numbers and steal from mobile wallets.
Central Bank data shows mobile banking was the hardest-hit channel by cyber fraud in 2024, with criminals siphoning KES 810.68 million ($6.27 million / £4.74 million), up from KES 182.41 million ($1.41 million / £1.07 million) in 2023. The thefts often occur on Friday and Saturday nights, with millennials most affected.
The Communications Authority of Kenya recorded 11.1 billion cyber threats in the year to June 2026, a 29% increase from 8.6 billion a year earlier.
Kenya’s current National Payment System Act was enacted in 2011 and is silent on cybersecurity. It does not require payment providers to report such breaches immediately. The Treasury and Central Bank say the law is no longer fully aligned with the pace of technological change.
“This creates regulatory gaps that hinder innovation while exposing the financial system to risks such as fraud, cybercrime, money laundering, and operational inefficiencies,” the apex bank and Treasury say.
The proposed law seeks to strengthen cybersecurity and technology risk management through enhanced incident reporting, threat intelligence, security testing, third party risk management and stronger supervisory arrangements.
Authorities also point to growing interconnection between banks, payment service providers, fintechs, payment systems and third party technology providers as a source of new risks.
“Rapid digitisation, increasing reliance on technology and growing interconnection between banks, PSPs, fintechs, payment systems and third-party technology providers, expose the payment ecosystem to cyber threats, fraud, operational disruption, data compromise and risks associated with emerging technologies and new business models,” the proposals say.
Other markets have adopted similar measures. The European Union requires payment service providers to report major operational or security incidents within four hours of classification, or within a maximum of 24 hours after becoming aware of an incident. Thailand requires payment providers to disclose cybersecurity incidents and data breaches under a framework overseen by the Bank of Thailand, the Personal Data Protection Committee and national cybersecurity authorities.
Kenya is one of only four African countries requiring cyber incident disclosure within 72 hours, alongside Nigeria, South Africa and Mauritius.
The current exchange rate as of 4th October 2026 is $1 = KES 129.28 and £1 = KES 171.35.
Discover more from Access Radio®
Subscribe to get the latest posts sent to your email.